The short version
- Australian federal authorities have charged two men with participating in cybercrimes associated with the hacking collective TeamPCP.
- The group deployed a malware worm known as Shai-Hulud, which infected more than 1,000 organizations by compromising continuous integration and deployment pipelines.
- Investigators suggest that artificial intelligence tools may have lowered the technical barrier for the attackers, allowing them to execute complex campaigns with reduced operational discipline.
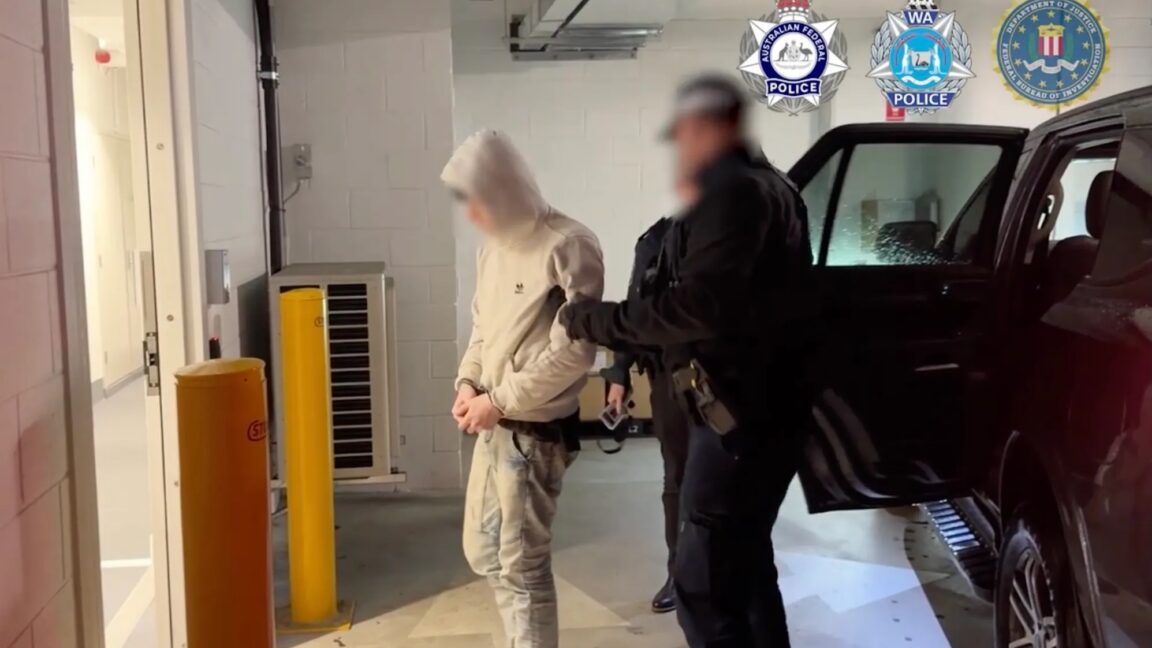
Federal police in Australia have arrested two men accused of involvement in a widespread cybercrime operation linked to the hacking group TeamPCP. The suspects, who reside in the Western Australian communities of Cottesloe and Mandurah, face fourteen criminal charges related to their alleged activities. While official statements from law enforcement did not release the identities of the defendants, independent security reporting has identified them and detailed the investigative path that led to their detention. If convicted, one individual could face a prison sentence exceeding twenty years, while the other faces a potential term of more than ten years.
TeamPCP has drawn significant attention from global security agencies since its emergence in December of last year. The group is credited with orchestrating a relentless series of supply-chain attacks that targeted the infrastructure used to build and distribute software. Over a nine-month period, these operations resulted in the compromise of more than 1,000 organizations worldwide. The scale of the intrusion highlights the vulnerability of modern software development practices, where trust in open-source components is often assumed rather than verified.
The primary weapon used by the group was a self-propagating malware worm dubbed Shai-Hulud. This malicious code targeted continuous integration and deployment pipelines, which are critical systems that allow developers to rapidly update and release software applications. Once a specific package or tool within these pipelines was infected, the malware attached itself to future updates. As developers downloaded and processed these compromised packages through their own systems, the infection spread further, creating a viral effect that moved from one organization to another.
A critical component of Shai-Hulud’s success was its ability to harvest credentials from the memory of infected hardware. By collecting access keys for other software packages, the attackers could then use those stolen credentials to infect additional targets. This method allowed the malware to bypass traditional security checks that rely on verifying the integrity of individual downloads. The worm’s design ensured that once a single point in the supply chain was breached, the compromise could cascade through multiple downstream projects.
One notable instance of this propagation involved the Trivy vulnerability scanner, a widely used tool for identifying security flaws in software. After Trivy was compromised, the malware spread to several other packages, including KICS, the Telnyx Python SDK, and LiteLLM. Developers who utilized these infected tools inadvertently introduced the malware into their own environments. The initial breach of the Trivy scanner alone resulted in the theft of terabytes of private data and credentials, underscoring the severe consequences of supply-chain vulnerabilities.
To maintain control over the infected machines, TeamPCP employed an unconventional technical strategy involving smart contracts on the Internet Computer Protocol. These canisters allowed the worm to locate command-and-control servers using URLs that could be changed rapidly, making it difficult for third parties to take down the infrastructure. Infected systems were programmed to report back to these control servers every fifty minutes, ensuring a steady stream of data and commands while evading detection.
Security researchers have noted that the operational methods of TeamPCP differ from those typically seen in high-level hacking groups. Traditionally, executing such complex campaigns requires extensive research, custom code development, and robust infrastructure management. However, investigators suggest that the use of large language models has significantly compressed the time and skill required to achieve these results. This technological shift may have enabled individuals with less traditional operational discipline to carry out sophisticated attacks.
The arrests mark a significant step in disrupting the activities of TeamPCP, but the broader implications for software security remain. The incident serves as a stark reminder of the risks inherent in relying on interconnected supply chains for software development. As organizations continue to adopt rapid deployment practices, ensuring the integrity of every component in the pipeline becomes increasingly critical. Law enforcement and security firms will likely continue to monitor for any resurgence of similar tactics or new variants of the Shai-Hulud malware.
The case also highlights the evolving nature of cyber threats, where artificial intelligence tools are lowering the barrier to entry for complex attacks. While the two suspects face serious charges, the global community must address the systemic vulnerabilities that allowed such a widespread infection to occur. Strengthening verification processes and improving detection mechanisms for supply-chain attacks will be essential in preventing future incidents of this magnitude.
Sources behind this briefing
Go to the original reporting
- Ars Technica↗Authorities arrest 2 alleged members of prolific hacking group TeamPCP

