The short version
- Android now supports secure, on-device migration of passwords and passkeys between compatible password manager applications.
- The feature eliminates the need for unencrypted CSV exports by using a new Credential Transfer API integrated into Google Play Services.
- Current support is limited to Google Password Manager, 1Password, Bitwarden, and Dashlane, with no timeline provided for broader adoption.
Google has introduced a new capability within the Android operating system that allows users to securely transfer login credentials between different password manager applications. This development addresses a longstanding friction point in digital security management: the difficulty of switching tools without compromising data integrity or enduring tedious manual entry. As password complexity requirements have increased, the burden on users to remember or manually re-enter long strings of characters has grown significantly. The new system aims to streamline this transition while maintaining high security standards.
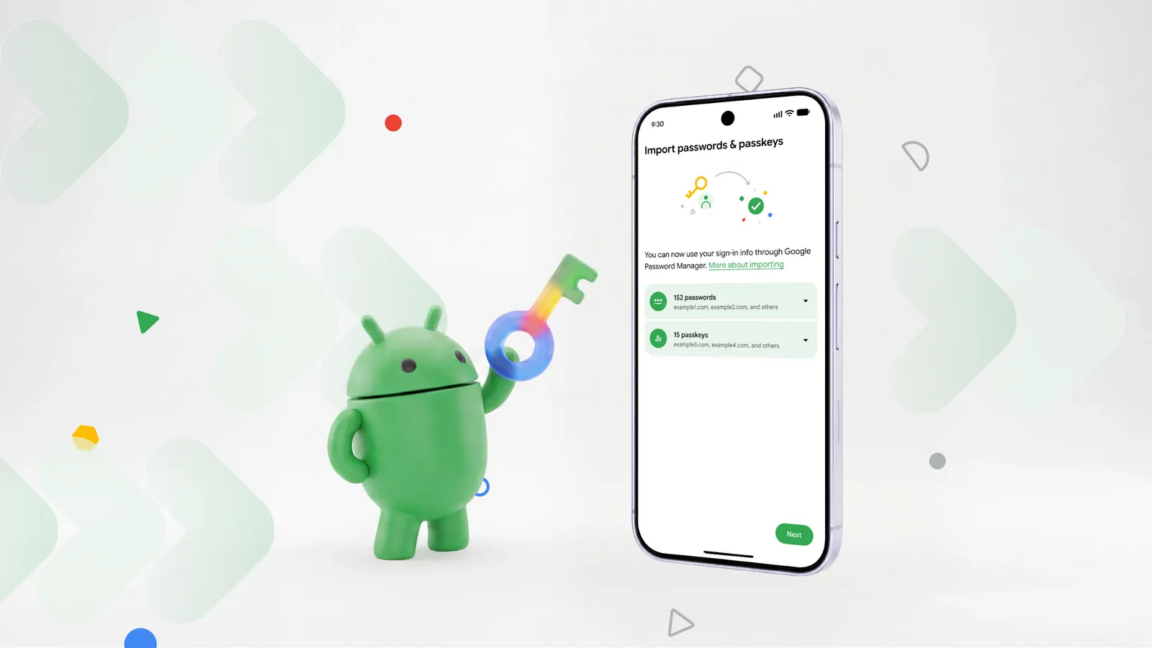
The migration process is designed to occur entirely on the user’s device, ensuring that sensitive data does not traverse external servers or leave the phone during the transfer. To initiate a move, users must have both the source and destination password manager apps installed with their credentials synced. The action begins in the application intended to receive the data, where an import option triggers the system-level migration protocol. In Google’s native Password Manager, this feature is located within the settings menu, though placement may vary across different third-party applications.
Security remains a central focus of this implementation. Unlike traditional export methods that generate unencrypted CSV files containing plain-text passwords, the new Android system handles both standard passwords and passkeys without creating risky intermediate text files. The operating system verifies the user’s identity before proceeding and requires explicit confirmation within the new password manager app. This end-to-end verification process is intended to prevent unauthorized access or data leakage during the transition period.
Compatibility with this feature relies on the Credential Transfer API, a framework that participating applications must implement to enable seamless data handoffs. Currently, only a select group of major providers supports this standard. Google Password Manager, which is built directly into Android, works alongside 1Password, Bitwarden, and Dashlane. Users attempting to migrate between these specific apps can expect the process to complete quickly, even when handling large volumes of stored credentials.
For users relying on password managers outside this initial group, the new system offers no immediate benefit. Those individuals remain dependent on manual entry or the creation of unencrypted CSV files, which pose inherent security risks if not handled carefully. Google has indicated that additional password managers will eventually add support for transfers via the Credential Transfer API, but the company has not provided a specific timeline for when these updates might arrive. This lack of clarity leaves many users in a transitional state where secure migration is not yet universally available.
The technical requirements for using this feature are relatively modest, contributing to its potential reach across the Android ecosystem. No operating system update is necessary beyond what is already widely deployed. The functionality is integrated into Google Play Services and is available on devices running Android 8.0 Oreo or higher. Since Play Services support extends back to Android 7.0 Nougat, the migration tool should function on virtually every operational Google-certified Android device currently in use.
This update represents a shift toward more user-friendly security practices within mobile operating systems. By removing the technical barriers and security risks associated with switching password managers, Google encourages users to maintain robust credential hygiene without being locked into a single provider. However, the limited initial support means that the full benefits of this system are not yet accessible to all Android users.
As the technology matures, the extent of third-party adoption will determine the long-term impact of this feature. If major competitors integrate the Credential Transfer API, the industry standard for password management could shift toward more secure and seamless transitions. Until then, users must carefully evaluate their current tools and consider the security implications of any migration method they choose to employ.
The introduction of this feature underscores the growing importance of interoperability in digital security infrastructure. While the immediate utility is constrained by the narrow list of supported applications, the underlying architecture provides a foundation for future improvements. Google’s decision to embed this capability within Play Services suggests a commitment to broadening access over time, even if the current rollout is cautious.
For now, the primary value lies in the elimination of unencrypted data exports for users of compatible apps. This change reduces the attack surface associated with credential management and simplifies the user experience. As more applications adopt the standard, the convenience and security benefits are likely to expand, potentially reshaping how consumers interact with their digital identities.
Sources behind this briefing
Go to the original reporting
- Ars Technica↗Android can now securely migrate your logins between password managers
