The short version
- Artificial intelligence models can identify the location of travel photos with up to 91 percent accuracy by analyzing visual details like architecture and signage.
- Fraudsters use this geolocation data to create personalized scam messages that claim unusual activity occurred at the victim's specific holiday destination.
- Security experts advise delaying social media posts until after returning home and avoiding links in urgent messages regarding account security.
A new wave of digital fraud is emerging that leverages artificial intelligence to exploit the visual data contained in vacation photographs. Criminals are increasingly using AI tools to analyze images posted on social media platforms such as Instagram and Facebook, extracting precise location information from background details. This capability allows them to craft deceptive messages that reference a victim's specific travel itinerary, lending an air of legitimacy to attempts to steal financial credentials.
The threat relies on the ability of modern AI models to interpret subtle visual cues that humans might overlook or consider insignificant. Researchers at McAfee conducted tests using two freely available AI systems to analyze more than 21,000 travel images. The results demonstrated that one model correctly identified the location in 91 percent of cases, while the other achieved an accuracy rate of 87 percent. These findings suggest that computers no longer require explicit metadata or user tags to determine where a photo was taken.
The technology works by scanning for recognizable landmarks, skylines, street markings, and even specific types of signage or storefronts. In some instances, the arrangement of flowers or unique architectural features can be enough for an AI agent to deduce the exact site. For example, in testing scenarios, an AI correctly identified a river scene as Hastings-on-Hudson in New York state based on foreground trees and water features. Another image of tulips was accurately linked to the Keukenhof gardens in the Netherlands due to the specific layout of the blooms.
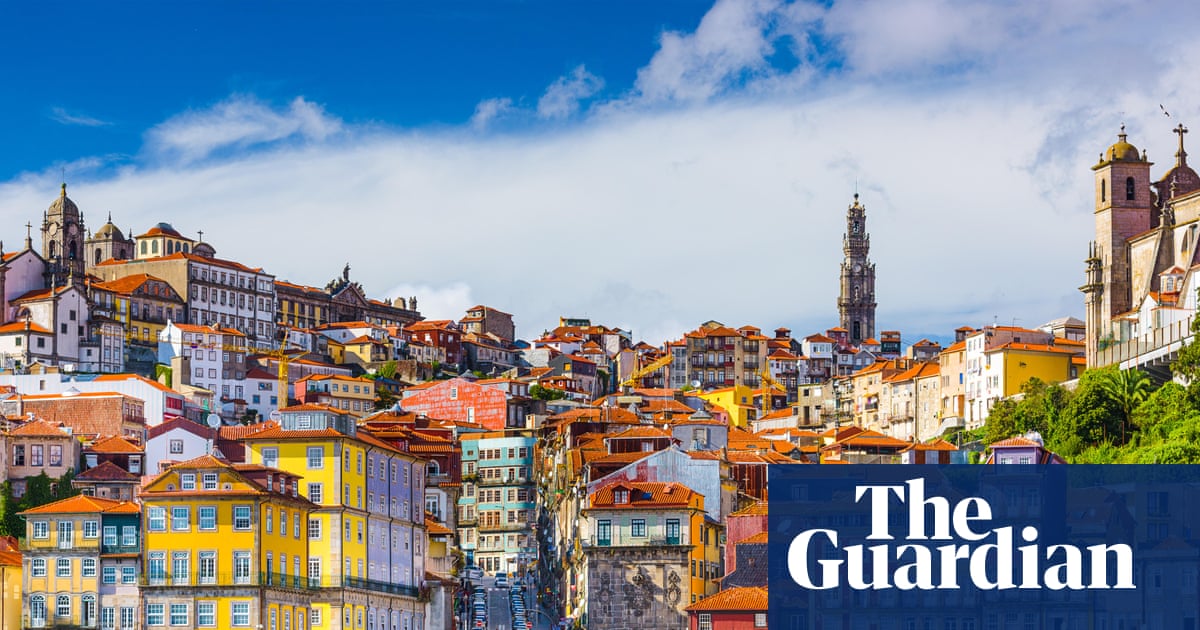
This precision provides scammers with powerful material for social engineering attacks. Instead of sending generic warnings about compromised accounts, fraudsters can now send texts or emails that mention a victim's recent trip to a specific city or country. A message might claim that unusual activity was detected while the user was traveling in Porto, or that an unauthorized login attempt originated from a hotel where the victim recently stayed. Because the location details are accurate, recipients are less likely to suspect foul play and more likely to click on malicious links.
The vulnerability extends even to photos that appear generic or lack obvious landmarks. While images taken on beaches or inside hotel rooms may lower the accuracy of pinpointing an exact address, AI systems can often still identify the country or region. This broader geographic identification is frequently sufficient for criminals to make their scams credible. The ease with which these tools operate has raised concerns among cybersecurity professionals about the privacy implications of sharing visual content online.
Staff members at McAfee who participated in the testing expressed discomfort upon realizing how easily their own travel histories could be reconstructed from seemingly innocuous pictures. The experiment highlighted that even when users believe they have obscured their location by avoiding geotags, the visual content itself remains a rich source of data for AI analysis. This shift underscores a growing gap between user expectations of privacy and the technical capabilities of automated image recognition systems.
Security experts recommend several precautions to mitigate this risk. One effective strategy is to delay posting vacation photos until after returning home, which removes the real-time element that scammers exploit. Users are also advised to adjust social media settings so that images are visible only to trusted contacts rather than the public. These steps can significantly reduce the pool of data available to malicious actors.
General vigilance remains critical in defending against these sophisticated scams. Recipients should be wary of any message that creates a sense of urgency or demands immediate action, as this is a common tactic used to bypass rational scrutiny. Instead of clicking on links provided in texts or emails, individuals should verify concerns by contacting their bank or service provider directly through official channels listed on websites or physical cards. As AI capabilities continue to advance, the intersection of visual data and financial fraud presents a persistent challenge for digital security.
The findings from this research serve as a warning about the unintended consequences of sharing personal moments online. While social media platforms facilitate connection and memory keeping, they also inadvertently provide raw material for automated systems designed to extract private information. Understanding how AI interprets visual context is essential for users who wish to protect their financial security in an era where digital footprints are increasingly scrutinized by both legitimate services and malicious actors.
Sources behind this briefing
Go to the original reporting
- The Guardian World↗‘We detected unusual activity’: the scam that uses AI to exploit your holiday photos